Jul – Aug 2026Tunis
Built a secure delivery platform on Kubernetes, from the first commit scan to runtime detection.
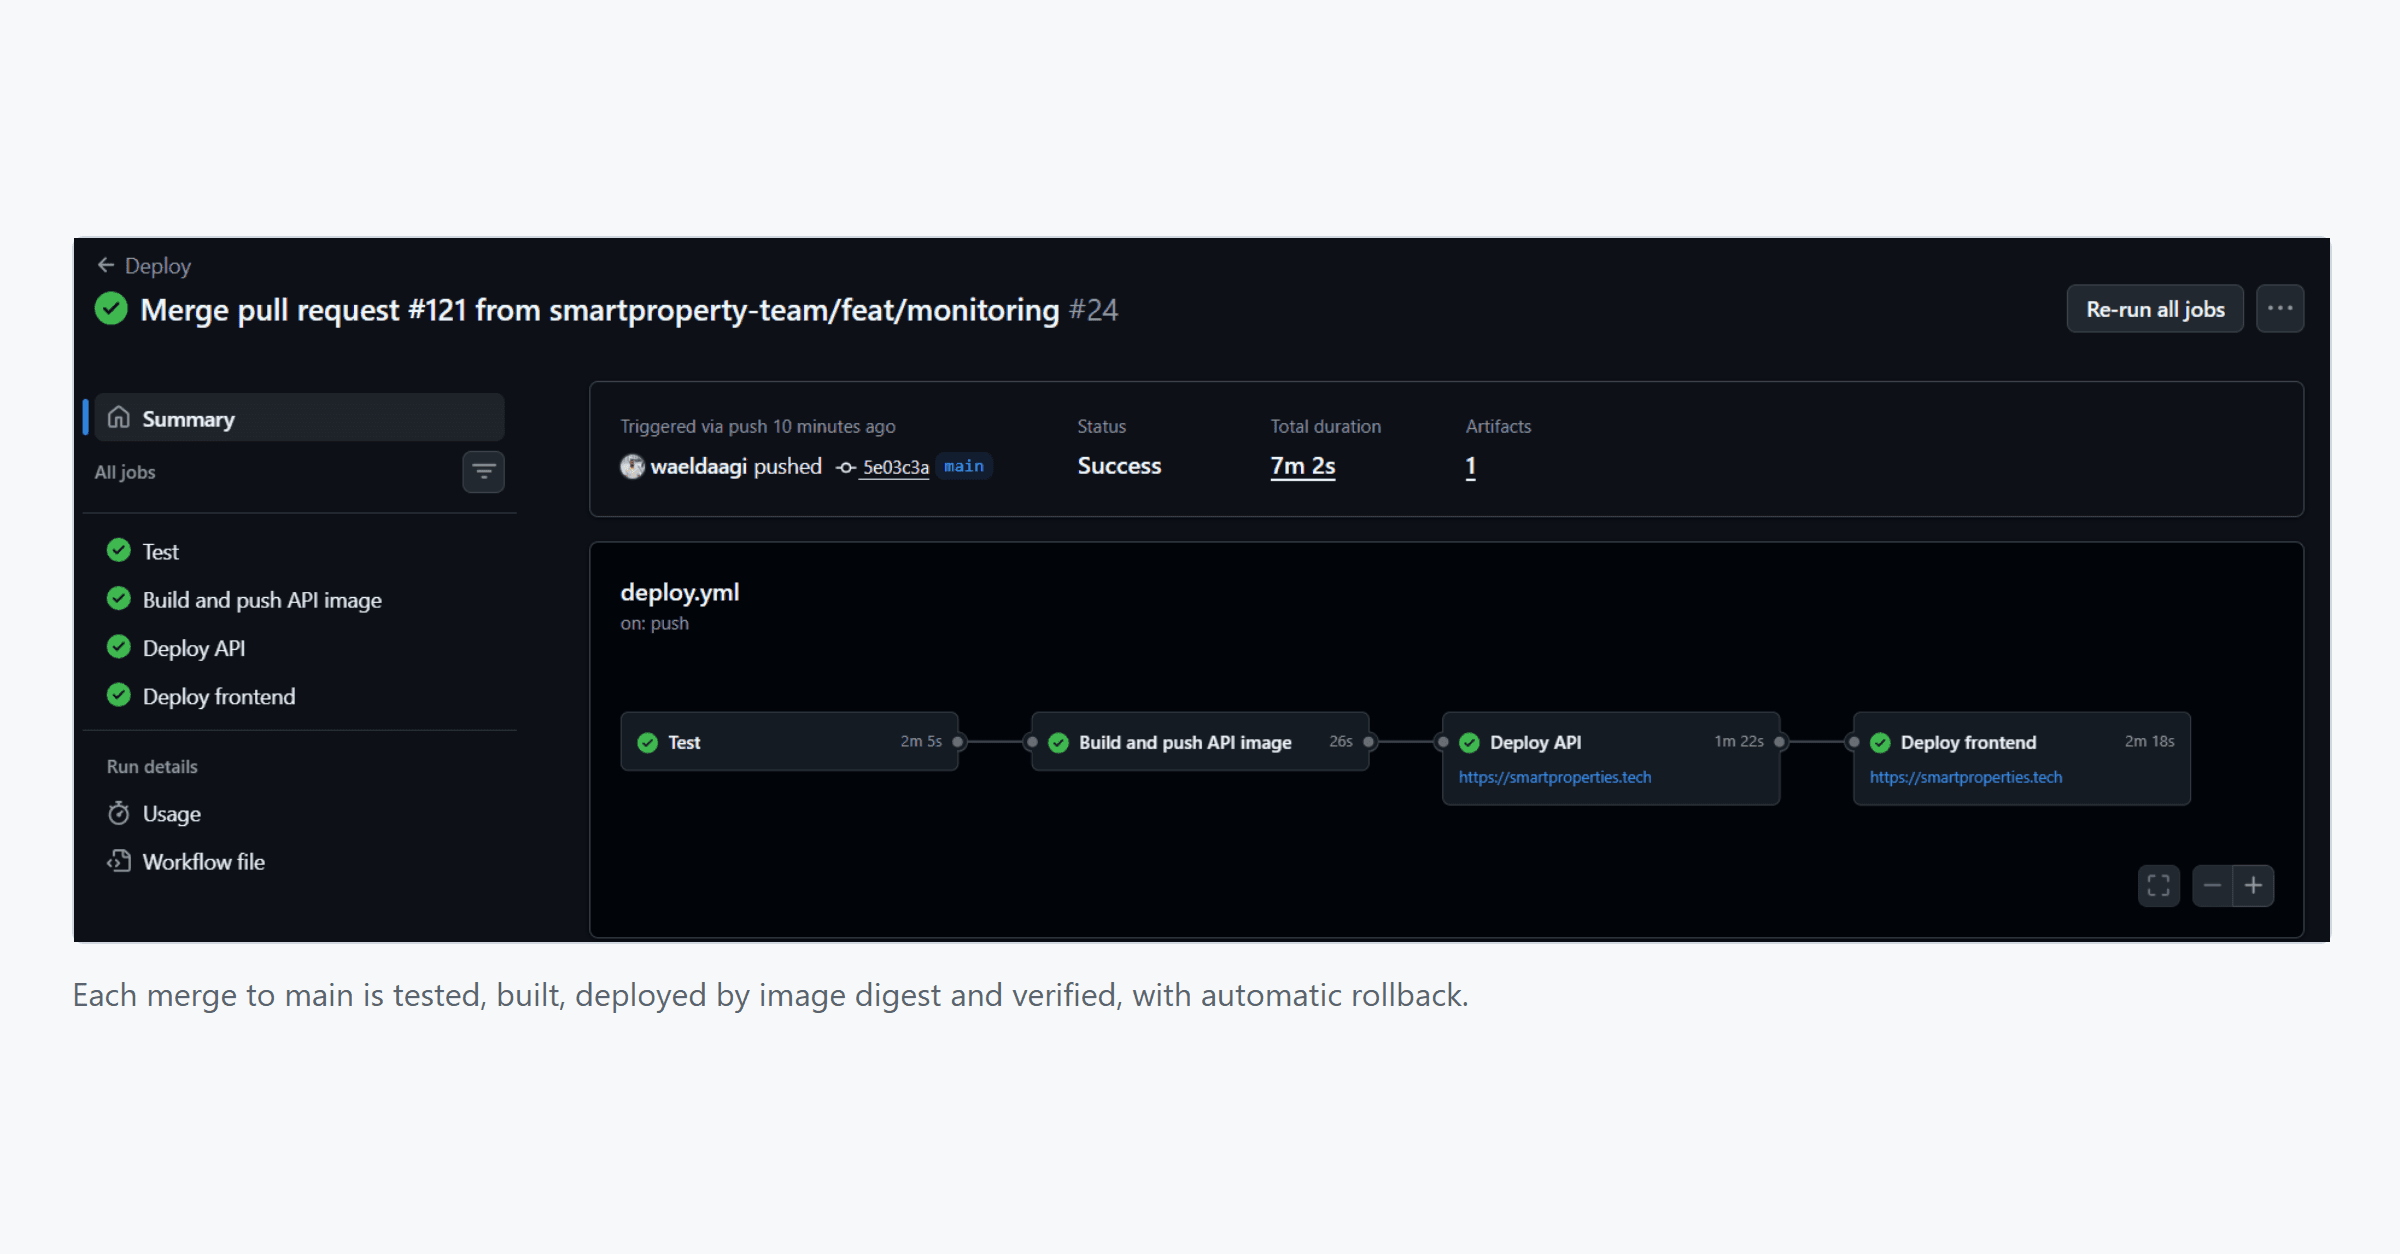
- Built a reusable 7-stage GitLab CI/CD component (secret scanning, dependency and container vulnerability scanning, image signing, Kubernetes signature verification) adopted by two projects; onboarding now takes six lines of YAML. Its first run caught a live AWS access key hidden in Git history.
- Migrated a NestJS and MongoDB service to production Kubernetes, fixing 4 security defects including root container execution and 2 critical CVEs (RCE, XSS); hardened the Dockerfile (npm ci, non-root user, tini).
- Delivered a production-ready Kubernetes platform in 9 phases, verified by 65 automated conformance checks, with Argo CD GitOps delivery; cut deployment latency from about 3 minutes to seconds with event-driven Argo Events.
- Configured merge-request pipelines with automated tests and security scans; debugged and fixed Docker-in-Docker TLS failures on self-hosted GitLab Runners (Linux, systemd).
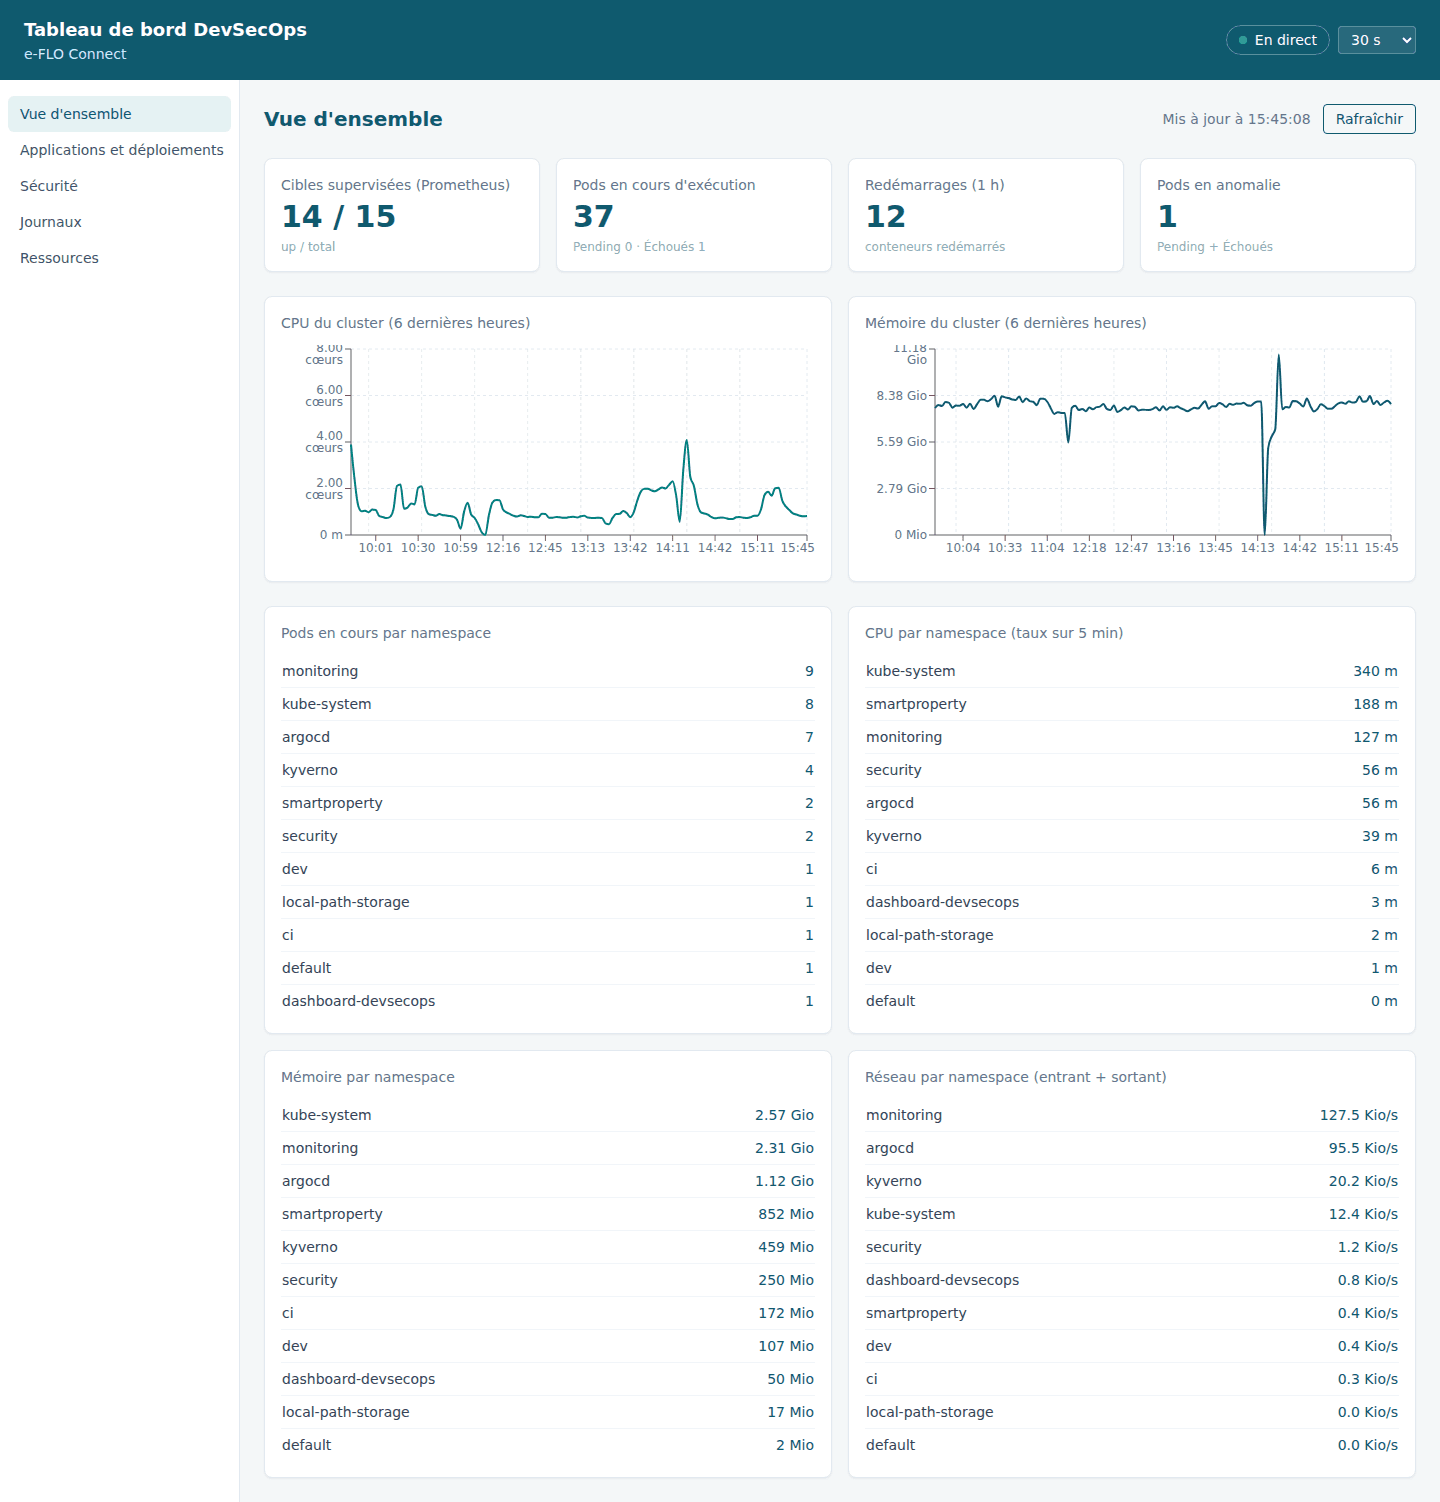
- Set up Prometheus, Grafana and Loki observability, and wrote the technical documentation, including disaster recovery.
- GitLab CI/CD
- Kubernetes
- Argo CD
- Kyverno
- Trivy
- Docker
- Prometheus
- Grafana